Illustration, AI-generated from the story text. Tap a panel to read the story through it.
Security firm Parameter published a flaw chain on October 28th that let a booby-trapped public ChatGPT share link run the attacker's JavaScript as chatgpt.com inside a signed-in victim's session, read the victim's private conversations and send them to an outside server. The victim only had to open the link.
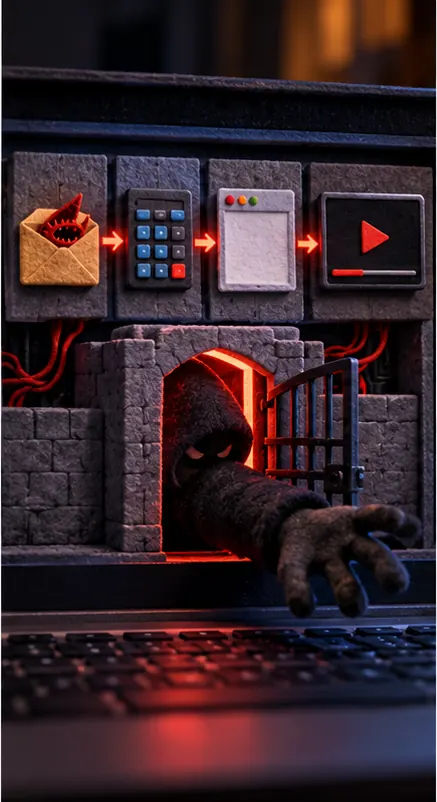
The chain joined a math-input component that accepted messages without checking the sender, an with no , and a YouTube embed that slipped past the site's content security policy.
Parameter reported it on October 18th. OpenAI raised its severity on October 21st, fixed both web frontends by October 26th and paid a $5,000 . Parameter tested only its own accounts, and there is no sign anyone exploited it.
Share links exist to be posted publicly, so one bad link could have reached anyone who clicked.
Opening a shared ChatGPT link was enough to hand over your private chats, until October 26th
Security firm Parameter published a flaw chain on October 28th that let a booby-trapped public ChatGPT share link run the attacker's JavaScript as chatgpt.com inside a signed-in victim's session, read the victim's private conversations and send them to an outside server. The victim only had to open the link. The chain joined a math-input component that accepted messages without checking the sender, an iframe with no sandbox, and a YouTube embed endpoint that slipped past the site's .
Parameter reported it on October 18th. OpenAI raised its severity on October 21st, fixed both web frontends by October 26th and paid a $5,000 bounty. Parameter tested only its own accounts, and there is no sign anyone exploited it. Share links exist to be posted publicly, so one bad link could have reached anyone who clicked. SourcesA
Sources
- AWe found a gap at OpenAI (Parameter)parameter.ai
This story ran in the Morning Brief of October 31st 2026.